










Short answer: Artificial intelligence should classify inspection evidence, show deficiencies and present suggestions to the expert. The conformity decision, the interpretation of a critical finding, exception acceptance and report publication must not be completed without the traceable approval of a competent human.
Why should the correct boundary be drawn per task?
The question “are we using artificial intelligence?” is not sufficient on its own. The real question is which task the system performs and what a faulty output leads to. Matching a photograph with the correct work order is not in the same risk class as deciding that equipment is fit for use.
Published by ISO in March 2026, ISO/IEC 17020:2026bases competence, impartiality and consistent operation for inspection bodies; in the new edition, risk-based thinking and the control of data and information also come to the fore. The technical result from this framework is: AI output should be designed not as an independent decision replacing the inspection method and competent personnel, but as a controlled process input.
Where does artificial intelligence produce safe value?
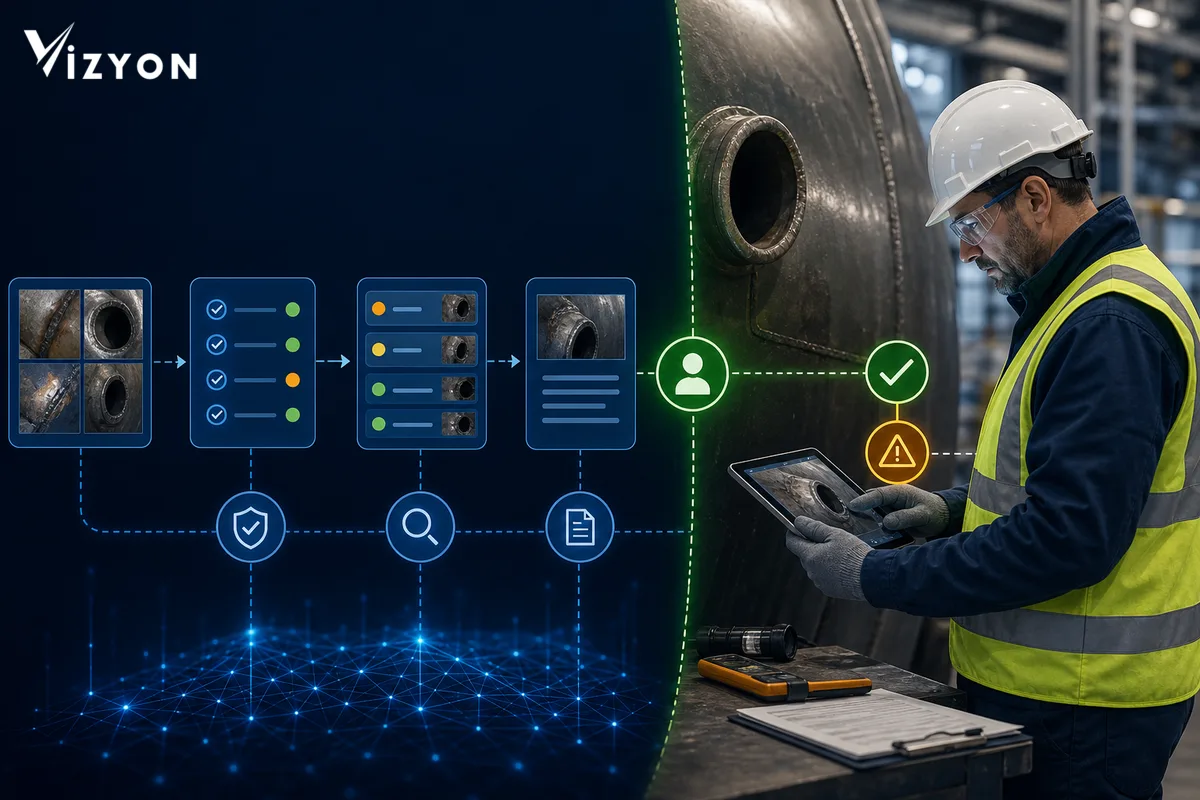
The most suitable areas are support tasks with reversible output where the expert can easily return to the actual evidence. Rejection of the system's suggestion must not disrupt the workflow; low confidence, data drift or missing evidence must automatically create a review queue.
- Record completeness check: Flagging deficiencies in mandatory fields, photographs, device records, personnel competency and time stamps before report publication.
- Anomaly prioritization: Ranking suspicious records that the expert should look at first among many measurements or images; not making a “defect exists” judgment.
- Document and evidence matching: Relating the field photograph to the equipment, checkpoint and work order; leaving ambiguous matches to a human queue.
- Draft generation: Creating a report summary or finding draft from approved fields; not publishing a sentence whose source it cannot show.
- Planning support: Suggesting a route or order with workload, location and duration data; not overriding hard rules such as competency, independence and device suitability.
The current online core of NIST AI RMF 1.0 requires the separation of human-AI roles, documentation of the system's information limits, definition of human oversight processes, and testing of systems before deployment and during use. In the VizyonTech workflow, its counterpart is keeping the model version, input evidence, confidence/exception status and human action in the same audit trail.
At which steps must human approval remain mandatory?
If the output affects safety, regulatory compliance, accreditation scope, customer rights or the official nature of the report, the human must not be merely a symbolic “approve” button. The competent person must be able to access the actual evidence, reject the suggestion, record the justification and stop the process.
| Task | AI role | Human gate | Fail-closed behavior |
|---|---|---|---|
| Photo and record classification | Suggestion | Verification of a low-confidence match | If the match is ambiguous, the record is not closed |
| Anomaly scanning | Prioritization | Interpreting the raw evidence and establishing the finding | The model result alone is not counted as a defect |
| Measurement acceptance | Consistency/limit warning | Evaluating method, device and condition suitability | With missing traceability the result cannot be used |
| Conformity decision | Evidence summary | Competent technical decision | The decision is not formed without human approval |
| Exception or deviation | Risk signal | Authorized justified acceptance/rejection | Without a time-limited and recorded approval, the process stops |
| Report publication | Draft and completeness check | Technical approval and, if required, signature | An unapproved version cannot be opened to the outside |
EU Artificial Intelligence Regulation 2024/1689 Article 14provides that, for high-risk systems, the oversight officer can understand the capacity and limitations, be vigilant against automation bias, interpret and disregard the output, and be able to stop the system. This article does not claim that every inspection use of AI is legally “high risk”; it uses these capabilities as a strong design checklist for critical inspection decisions.
How does human approval become a real control?
Writing a name on an approval screen is not enough. For effective control, the task, the authorization and the evidence must meet in the same place:
- Define the role in advance: Link who can give approval in which method, scope and decision type with the competency record.
- Show the actual evidence: Let the expert see not only the AI summary but the photograph, raw measurement, device, method and past revisions.
- Do not hide ambiguity: Let the model version, evaluation time, performance threshold and the reason for low confidence be present in the audit trail.
- Make rejection possible: The powers to modify the suggestion, reject it, send it to a second review and make an emergency stop must be real.
- Measure automation bias: How often humans accept the suggestion without evidence, missed findings and false alarm examples should be periodically reviewed.
Addressed to inspection bodies, ILAC P15:05/2020is the current ILAC document explaining the accreditation application of ISO/IEC 17020:2012. Even though ISO's 2026 edition has been published, the organization's transition plan and its own accreditation authority's current regulations must additionally be verified. For this reason, the software must not assume the standard version as fixed; it must keep the method, scope and transition rule configurable.
How are data security and privacy protected?
Field photographs, customer information, personnel records and report content must not be sent uncontrolled to a general-purpose model. The KVKK's Generative Artificial Intelligence and the Protection of Personal Data Guidedated 24 November 2025 emphasizes a human-centred, transparent and auditable approach; the assessment of personal data processing throughout its entire life cycle.
In technical practice, data minimization, role-based access, logging of the transfer destination, retention period, third-party provider assessment and the deletion/anonymization flow must be established together. Model input and output must not form a shadow archive escaping access control.
Example control architecture in the VizyonTech workflow
Vizyon Periyodik in a field-focused flow like this, the AI layer can produce evidence completeness and anomaly priority after the work order and the competency and device gates. However, the technical decision, version lock and report publication must remain in the existing authorized approval chain. Similarly, in NDT report management the method-specific raw evidence must be preserved independently of the AI summary.
The minimum audit trail should include the work order identity, data source, model and rule version, time, suggestion, confidence/exception information, the evidence viewed by the human, the acceptance/rejection action, the justification and the published report version. If the model is inaccessible, the critical decision path must continue manually and safely; automatic publication with missing evidence must not be made.
Evidence matrix
| Claim | Source | Date / version | VizyonTech counterpart | Technical result |
|---|---|---|---|---|
| Inspection confidence is based on competence, impartiality and consistent operation | ISO, ISO/IEC 17020 | 2026, 3rd edition; corrected version 2026-06 | It is an AI support layer | The conformity decision is locked in the competent role |
| Human-AI roles, limits and oversight must be documented | NIST AI RMF Core | AI RMF 1.0, 2023; online resource access 2026 | Role, model, input and audit trail | The suggestion becomes rejectable and testable |
| In critical oversight, the human must be able to disregard the output and stop the system | EU 2024/1689 Article 14 | 2024; the implementation timeline varies by use/scope | Override, stop and second review | Effective control is established instead of symbolic approval |
| The accreditation application of ISO/IEC 17020 is interpreted additionally | ILAC P15 | 05/2020 | Version and transition rules are made configurable | The old/new standard transition is not assumed |
| Personal data impacts must be assessed throughout the AI life cycle | KVKK Generative AI Guide | 24.11.2025 | Minimization, access and retention controls | Field data is not transferred to the model uncontrolled |
Final word
Good AI design in inspection is more concrete than the slogan “keep the human in the loop”: it accelerates low-risk preparation work, leaves the critical decision to the competent person and links every action of both with evidence. In the first pilot, select a single task; put in writing, before going into production, the cost of error, the escape condition, the human authority and the success criterion.
Sources
- ISO — ISO/IEC 17020:2026, Conformity assessment — Requirements for bodies performing inspection (March 2026; corrected English version June 2026).
- ILAC — ILAC P15:05/2020, Application of ISO/IEC 17020:2012 for the Accreditation of Inspection Bodies.
- NIST — Artificial Intelligence Risk Management Framework (AI RMF 1.0), NIST AI 100-1 (26 January 2023).
- NIST AIRC — AI RMF Core: Govern, Map, Measure, Manage.
- EUR-Lex — Regulation (EU) 2024/1689, in particular Article 14 (13 June 2024).
- Personal Data Protection Authority — Generative Artificial Intelligence and the Protection of Personal Data Guide (in 15 Questions) (24 November 2025).