










How is a bulk e-signature queue kept secure?
Fix each signing job with the document summary, version, signer, and a unique transaction key; verify authorization at the moment of execution, deduplicate repeats, and count only verified output as success.
When volume increases, the goal is not merely to speed up the queue. A state machine is needed that prevents the same document from being signed twice, a modified PDF from advancing with an old approval, a transient service error from looking like permanent success, and signature evidence from being detached from the business record.
With what identity should a signing job enter the queue?
The job identity must be based not only on the file name but on the document identity, immutable version, cryptographic digest, signer identity, signature policy, and intended transaction type.
BTK's current page explaining the framework of Law No. 5070 states that a secure electronic signature makes it possible to detect subsequent changes in the signed data. BTK's technical FAQ content also explains the requirements that the data to be signed must be viewable by the signatory before signing and that the signature creation data must not be extracted from the device. The consequence for queue design is clear: if the PDF is regenerated after a user approves a version, the same job must not continue; a new approval must be opened with the new digest. [1] [2]
| Field | Why is it required? | Transition rule |
|---|---|---|
| Document identity and version | Shows which controlled output the job belongs to. | If the version changes, the current job is set to cancelled; a new job is opened. |
| Document digest | Binds the approved bit sequence to the signature input. | The consumer recomputes the digest before signing; it stops if it does not match. |
| Signer and role | Enables authorization to be evaluated for the specific document and transaction. | If the role or certificate is unsuitable, the job does not proceed to the signing stage. |
| Idempotency key | Prevents a repeat of the same logical request from producing a second signature. | The same key returns the recorded result; it creates no new side effect. |
| Policy and format version | Preserves which validation rule was applied. | A rule change does not silently reinterpret open jobs. |
| Status and operation trail | Enables reconstruction of every transition from acceptance to archive. | Only permitted status transitions are enforced server-side. |
Which statuses must be kept separate in the queue?
The trio "pending, success, error" is insufficient; acceptance, pre-check, human approval, signing, verification, archiving, and review statuses must be separate.
- Accepted: Source document, version, digest, and idempotency key are recorded atomically.
- Pre-check: Document access, format, ownership, signer role, certificate selection, and policy compliance are audited.
- Awaiting approval: The signatory views the correct version of the document to be signed and gives approval for the specific transaction.
- Signing: A worker takes the task with a short-lived job lock; even if the lock expires, the idempotency record prevents a second side effect.
- Verifying: The generated signature is technically verified in the context of the signed document and certificate.
- Archived: The signed output, verification result, timestamp evidence, and operation trail are stored in the same record link.
- Review required: Ambiguous verification, permanent error, or contradiction is assigned to an authorized person without being converted to automatic success.
The OWASP transaction authorization guide recommends keeping meaningful transaction data on the server, executing steps in order, and having a unique authorization bond for each transaction. This means the queue consumer must not trust a "confirmed" field coming from the browser; it must re-verify the document digest, authorization, and status transition from the server record. [5]
How is retry done without producing double signatures?
Retry only transient errors, in a limited and delayed manner; bind each attempt to the same idempotency key and record the external signature result atomically.
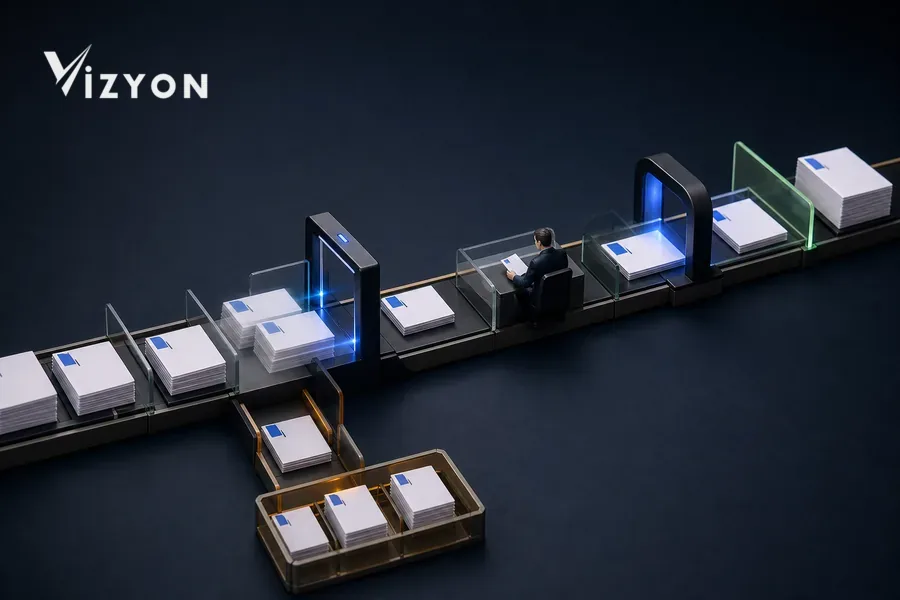
The OWASP Business Logic Security guide recommends storing the idempotency key transactionally together with the result for external and state-changing calls. If the network connection drops after the worker sends the request to the signing service, the assumption "no response came, so nothing happened" is dangerous. First, a recorded result or provider transaction identity with the same job key should be queried; only if it is proven that the transaction did not occur should it be resent. [4]
Classify errors: short-term connection loss and explicitly declared transient load on the service can be retried; an unauthorized user, changed document digest, invalid certificate selection, or verification failure must not be automatically repeated. Delayed retries can use increasing wait and random jitter; however, the attempt count and total duration should be set according to the organization's service target and risk assessment, and no unsourced universal number should be declared.
When is a job truly considered successful?
The creation of the signed file is not success on its own; the signature value, document link, signing certificate, verification policy, and, if applicable, the timestamp result must be recorded together.
ETSI EN 319 102-1 V1.4.1 defines the inputs and outputs of AdES creation and validation processes; it shows that in the validation outcome, success, failure, and indeterminate statuses are not the same thing. In the VizyonTech workflow, the worker must not close the job merely because the file was written; it must store the validation rule and result used and move failed or indeterminate results to the review queue. [3]
RFC 3161 defines the timestamp as a request-response protocol that provides evidence that data existed before a particular time. Therefore, if a timestamp is required, a mere "requested" record must not be kept; the message imprint, response status, returned token, and validation result must be linked to the same signing job. A mismatched nonce or document digest, a delayed response, or a rejected request must not be counted as success. [6]
The need for long-term validation depends on format, policy, and retention period. Rather than assuming the same archival profile for every signature, the organizational procedure and applicable technical criteria should be applied as a versioned policy.
How should the system protect load and the signatory?
When the acceptance rate exceeds signing capacity, do not accumulate unlimited work; apply per-customer/organization quotas, priorities, backpressure, and visible aging metrics.
- Fair capacity: One customer's large batch must not indefinitely delay other organizations' jobs; tenant and priority limits must be explicit.
- Backpressure: When the queue reaches the defined operational threshold, acceptance of new batches should be slowed or scheduled.
- Job age visibility: An average alone is not sufficient; the oldest pending job, age per status, retry count, and review queue should be tracked separately.
- Short lock, permanent record: The worker lock is temporary; the job identity, attempt history, and result must be permanent.
- Safe observability: Logs must not contain document content, access data, PINs, private keys, or unnecessary personal data.
- Controlled cancellation: A job not yet signed can be cancelled; if the signature has been created, the status and distribution decision are taken to authorized review without deleting the output.
Which scenarios should be tested before going live?
Run not only the success flow but, with evidence, the worker crash, timeout, double delivery, document change, lost authorization, and indeterminate verification scenarios.
- When the same idempotency key arrives with two concurrent requests, is only one signature output produced?
- When the signature call completes but the response is lost, does the retry find the recorded result?
- If the document changes after approval, does the digest check stop the job and request a new approval?
- If the signer's role or certificate status changes while waiting, does the consumer re-evaluate this?
- When the verification result is indeterminate, does the system not send a success delivery notification?
- Can a job in the error queue be restarted by an authorized person while preserving the reason and previous attempts?
- Can the archive record show the signed output, verification result, timestamp, and operation trail under the same version?
How does VizyonTech handle this flow?
VizyonTech configures the steps from report production to human approval, from the e-signature queue to verification and archiving, together with the organization's roles, document versions, and exception rules.
In bulk signature design, we first elicit the real document types, signer roles, certificate and timestamp policy, service outage scenarios, and delivery channels. We then validate the unique job identity, permitted status transitions, retry behavior, review queue, and visible operational metrics in a pilot document flow.
how to later correct a signed report in the e-signed report revision guide; how the end user can check the current output is covered in the report verification page guide . To plan a secure pilot with your organization's document volume and error scenarios, You can contact VizyonTech.
Sources
- BTK — Electronic Signature General Information (page dated January 16, 2026; framework of Electronic Signature Law No. 5070).
- BTK — Frequently Asked Questions on E-Signature (explanations of Law No. 5070 and the secondary regulation dated January 6, 2005).
- ETSI — EN 319 102-1, Procedures for Creation and Validation of AdES Digital Signatures; Part 1 (V1.4.1, June 2024).
- OWASP — Business Logic Security Cheat Sheet (idempotency, atomic transitions, and race condition checks; checked July 25, 2026).
- OWASP — Transaction Authorization Cheat Sheet (server-side authorization, binding to transaction data, and uniqueness; checked July 25, 2026).
- IETF RFC Editor — RFC 3161, Internet X.509 Public Key Infrastructure Time-Stamp Protocol (August 2001; updated by RFC 5816).
Sources were checked on July 25, 2026. In practice, current BTK regulations, organizational procedure, signature policy, the CSP used, and format validation rules must additionally be confirmed.